 NL
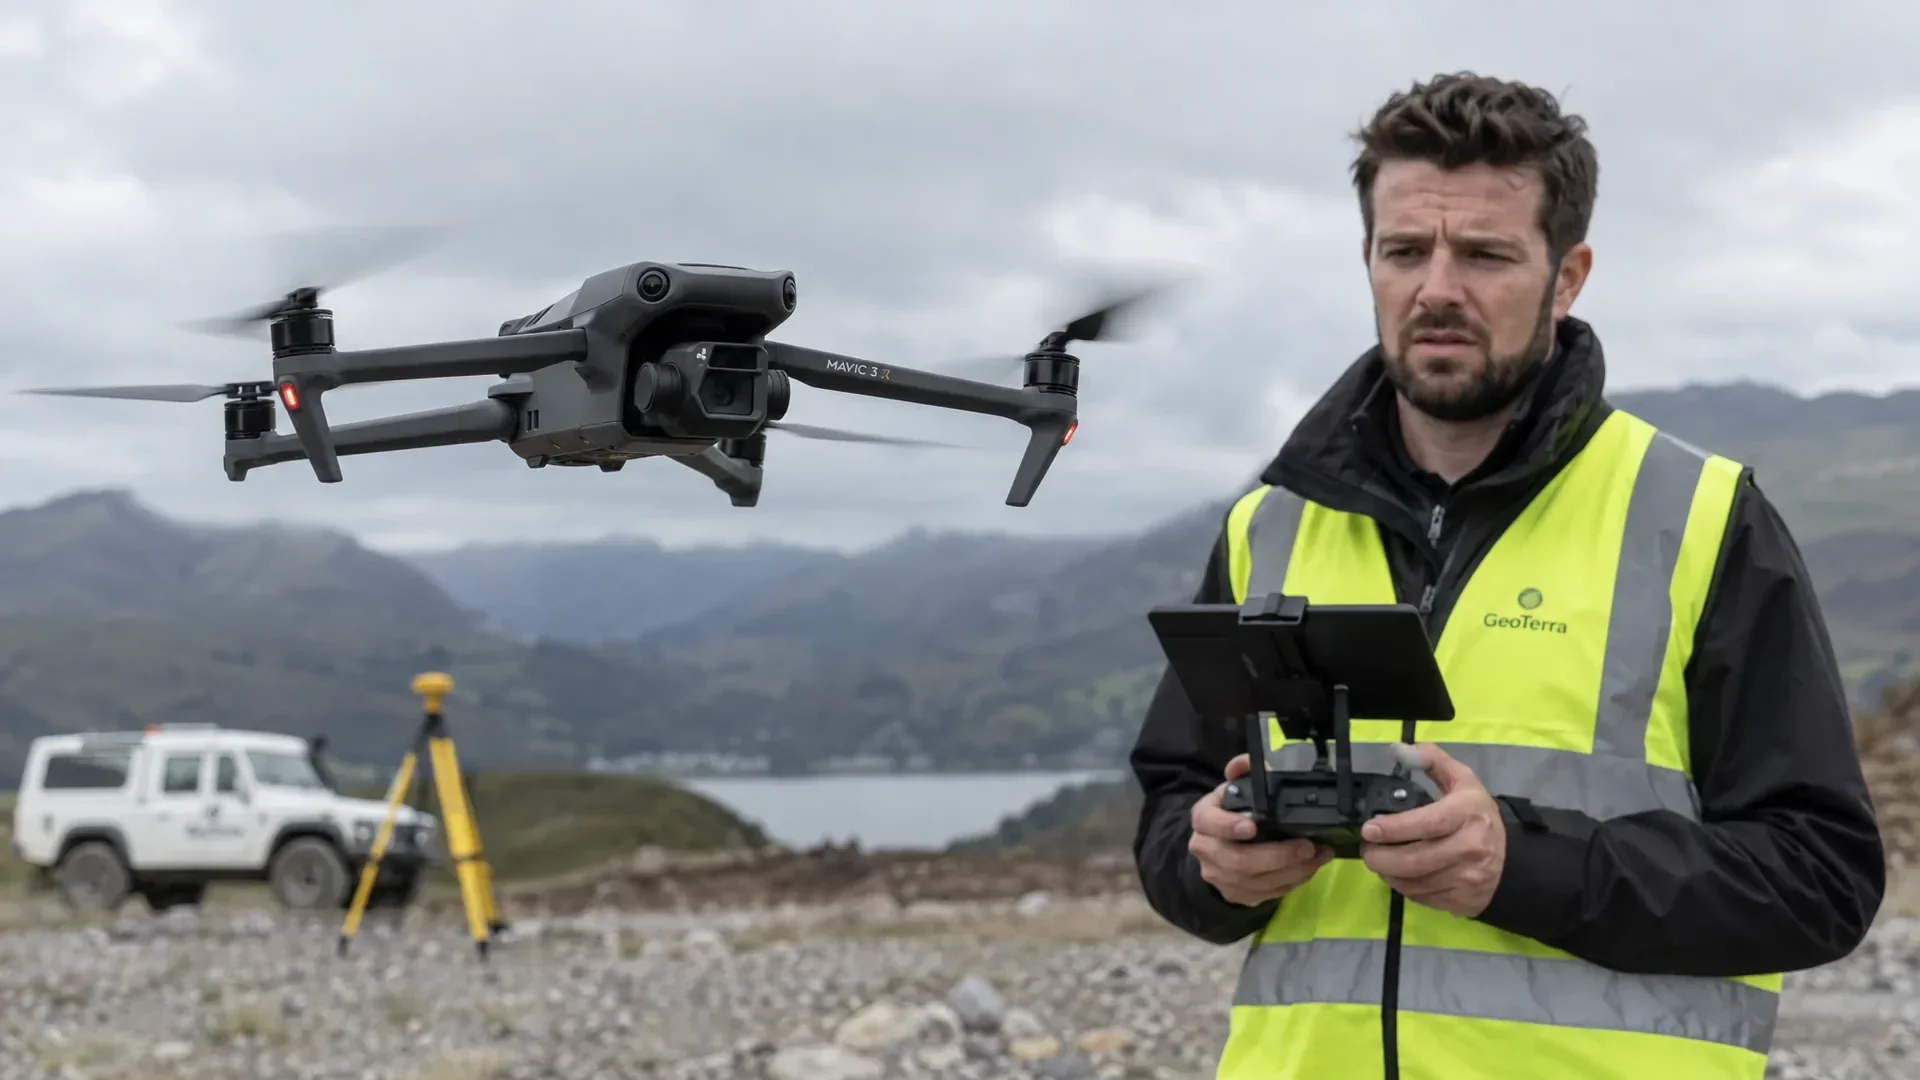
A flaw in the Bluetooth interface of DJI drones makes it possible to send commands to an aircraft without authentication. The vulnerability is registered as CVE-2026-78306 and carries a CVSS 4.0 score of 8.5 out of ten. Sixteen models are affected, from the Mini series and the Neo up to the professional Mavic 4 Pro. For most users the practical fix is a firmware update; for commercial operators it is a useful moment to revisit the cybersecurity part of their operating routine.
That nuance matters. A drone stopped being just a flying camera long ago: it is a networked device that communicates continuously with controllers, apps and sometimes cloud services. Every extra interface is extra attack surface, and this flaw can disrupt the link every commercial flight depends on.
What was found in the Bluetooth interface
The vulnerability was discovered by security researchers Abdelrahman Yousef and Dr Jordan Samhi. The error lies in how DJI implemented authentication for Bluetooth commands. Bluetooth is used here to connect to the aircraft's wifi interface and to exchange network data, but only some commands are checked against a trusted UUID. Other instructions can be offered without that validation.
Anyone physically within Bluetooth range can therefore send instructions using DJI's own DUML protocol. This is not an attack over the internet: the attacker has to be a few tens of metres away.
Which commands an attacker can send
According to the researchers, the unauthenticated commands go beyond reading information. They can change the wifi SSID and password, adjust wireless settings, and switch wifi or Bluetooth off and on again. The aircraft and various configurations can also be reset.
Some reset commands touch the flight controller, the gimbal, the camera, the wifi module and the software-defined radio; others can format storage or erase system logs. In their proof of concept the researchers added an extra confirmation step for dangerous commands, because resetting the flight controller can restart the motors.
Is mid-flight takeover plausible
Many headlines suggest a drone can be taken over during flight. Technically that is a possible consequence of the vulnerability, but it was not demonstrated in the published proof of concept. The researchers describe only a theoretical route: change the wifi password, connect to the internal network and from there possibly find a path to the flight controller. There are no indications that CVE-2026-78306 is exploited in practice; it does not appear in CISA's Known Exploited Vulnerabilities catalogue.
What the researchers do consider a concrete risk is an attack that only breaks the link between drone and pilot. An attacker can disable or restart wifi or Bluetooth, disrupting control, video feed and telemetry. Losing the C2 link is exactly the scenario your emergency procedures were written for.
The sixteen affected models and the firmware update
The CVE record lists sixteen affected models. A firmware update is indicated as the resolution for every affected aircraft, with the specific vulnerable firmware versions listed per model in the register.
| Model group | Affected models | Practical relevance for professionals |
|---|---|---|
| Compact and vlog drones | Neo, Neo 2, Flip | Widely used as a second aircraft for behind-the-scenes and fast social content. |
| Mini series | Mini 2, Mini 3, Mini 3 Pro, Mini 4 Pro, Mini 5 Pro | The C0 and C1 class aircraft flown by a large share of the European operator base. |
| Air and Avata series | Air 3, Air 3S, Avata 2, Avata 360 | Often used for dynamic and FPV-style shots on location. |
| Mavic 3 series | Several Mavic 3 variants | Workhorse for inspection, real estate and commercial video production. |
| Mavic 4 Pro | Mavic 4 Pro | Current high-end aircraft in many professional fleets, including cinematic work. |
DJI published a security advisory and updated the firmware. Notably, the changelogs do not qualify the fix as more than a known issue, so it is hard to verify whether a given update addresses this vulnerability. Compare the CVE record versions against your own fleet register instead of relying on the changelog text.
What this means for the European market and enterprise fleets
The flaw is not isolated. In August the same researchers reported several issues in DJI drones, including a media server reachable without login and an FTP service with a built-in password identical across all devices. Earlier work showed DUML data could be transmitted over Bluetooth unencrypted, and this year a flaw in DJI's SkyPixel platform was covered in our own technical analysis.
Such flaws are not new: in 2025 vulnerabilities in Holy Stone drones were documented, and back in 2015 the Parrot AR.Drone turned out to be takeover-able. What makes this case different is the scale at which the affected models fly in professional fleets: the Mavic 3 series and Mavic 4 Pro are production tools, not toys.
That connects the flaw to a wider European debate about dependence on a small number of manufacturers. The European Commission is working on its Drone Strategy 2.0, tariffs on drone components from China are in play, and in the United States there is a similar discussion about DJI's market access. Whatever the outcome: business-critical operators must be able to show their fleet firmware is current and managed.
EASA, SORA and where cybersecurity fits in your risk assessment
Under the European rules from EASA, the SORA methodology itself does not change because of a firmware flaw; the risk assessment remains built on ground risk, air risk and containment requirements. The subject is nevertheless hard to separate from the Specific category: anyone flying under an operational authorisation or a PDRA has described how the command and control link works and what happens if it is lost. That is explained in our piece on SORA 2.5 and containment levels, with the current texts in EASA's Easy Access Rules.
A firmware vulnerability that makes it possible to disable the C2 link therefore belongs in the same chapter as your mitigations for link loss: record which firmware versions are active and how updates are applied. For most organisations this is an extension of existing safety management rather than a new system.
There is a commercial reality alongside it. Clients in critical sectors, from grid operators to airports, increasingly ask about information security in procurement. The European Union Agency for Cybersecurity (ENISA) has long pointed to the growing attack surface of mobile apps and cloud integrations. An operator who can demonstrate sound firmware management stands stronger in those tenders. Our certified drone pilots therefore work with documented patch and fleet management.
A practical checklist for firmware and fleet management
The measures you can take now are largely the same as for any other networked device at work:
- Check the firmware version per aircraft: compare the drone, controller and app against the CVE record. If in doubt, update everything and verify the new version is running.
- Keep a fleet register: record which firmware each aircraft runs and when it was applied, so audits and client questions are answered quickly.
- Disable unused wireless interfaces: if Bluetooth has no function during flight, it does not need to be on.
- Never leave a powered aircraft unattended: the attack range is limited to tens of metres; a drone sitting with its battery installed in public is an unnecessary risk.
- Control physical access: cordon off and supervise the staging area when shooting in busy or publicly accessible locations.
- Avoid public networks for updates: apply firmware from a secured workstation, not from the guest wifi on location.
- Include it in the briefing: make clear that unusual wireless activity is a reason to stop the flight and report it.
For larger fleets it pays to bring flight preparation and documentation into one system. A platform such as DroneDeck combines airspace maps with flight plans, risk assessments and checklists, so firmware versions and maintenance history sit in the same file as the flight itself.
Three real-world situations where this flaw matters
It helps to translate the risk into daily practice:
- Film shoot in a busy city: the drone waits powered on at a publicly accessible staging point while lighting is set up. Passers-by are well within Bluetooth range, which calls for a cordoned-off staging area.
- Inspection of critical infrastructure: at a bridge or high-voltage station you often fly with a pilot and an observer. A broken C2 link mid-inspection means lost time and rebuilding the flight.
- Event or drone detection task: where several wireless systems are active at once, the chance of unintentional interference is higher. Strict frequency planning, as in cinematic drone operations, becomes even more important.
From firmware to flight safety
Enterprise clients read this news too and will ask whether the supplier is certified, how firmware is managed and what happens if the link is lost. On the data question, see our explanation of privacy and DPIA guidelines for drone flights.
The core of this incident is ultimately not dramatic: a flaw was found, reported, documented, and a firmware update is available. What it does show is where the weak link sits in the modern drone chain. As aircraft gain more connections, the number of ways something can go wrong without any relation to flying skill grows with it.
For professional operators that means a small expansion of the craft: alongside airspace knowledge, flying skill and SORA documentation, consistent firmware management now belongs in the same set. That is not a technical luxury, but part of the safety thinking that underpins an operational authorisation.
Frequently asked questions about CVE-2026-78306 and DJI firmware
Can an attacker really take over my drone mid-flight?
A full takeover during flight was not demonstrated. What the researchers did show is that anyone within Bluetooth range can send unauthenticated commands, for example to disable or restart wifi and Bluetooth, or to reset configurations. Losing the link between controller and drone is already a serious safety event on a commercial flight.
Which DJI models are affected by CVE-2026-78306?
The CVE record lists sixteen models, including the Neo, Neo 2, Flip, Air 3, Air 3S, Avata 2, Avata 360, several Mavic 3 variants, the Mavic 4 Pro and the Mini 2, Mini 3, Mini 3 Pro, Mini 4 Pro and Mini 5 Pro. A firmware update is available for every affected model.
How do I check whether my drone is still vulnerable?
Compare the firmware version of your aircraft and controller against the versions listed as vulnerable in the CVE record. If in doubt, update the aircraft, the remote controller and the app, then verify the new version is actually installed. Record the updates in your maintenance log.
What if I cannot disable Bluetooth for my workflow?
In that case, limit the time the aircraft sits powered on and unattended, keep it inside your controlled work area and keep firmware current. For business-critical operations, disabling wireless interfaces outside flight is the safer choice.